 Jan 12, 2025
 5 min read
Ansible 101
Ansible is an open-source Continuous Deployment, Configuration Management, & Orchestration. This tool aims to provide large productivity gains to a wide variety of automation challenges and is powerful enough to automate complex multi-tier IT application environments. Playbooks in Ansible are written in YAML format. It is a human-readable data serialization language that is commonly used for configuration files. It can also be used in many applications where data is being stored.
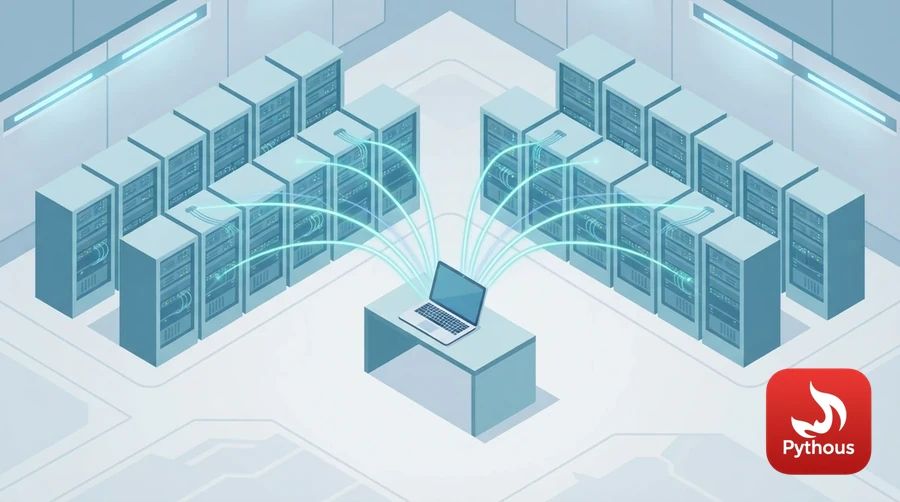
Illustration: one control machine configuring many servers at once.
Structure
- playbook.yml
- hosts
- roles/
nginx/ # Role name
tasks/ # Task directory
main.yml
nginx.yml
handlers/
files/ # 'copy' will refer to this
nginx.conf
templates/ # 'template' will refer to this
ssh.conf.j2
meta/ # Role dependencies here
vars/
main.yml
defaults/
main.yml
Connection
ssh-copy-id -i [email protected] # Copy SSH Key
ansible -m ping <host> # Check a specific host
ansible -m ping all # Check all hosts
Inventory
/etc/ansible/hosts # Default location
ansible-playbook -i hosts main.yml # Custom location
# Basic format of host file:
[web-servers] # A group
10.7.0.1 # A host
10.7.0.2 # Another host
Basic Commands
touch main.yml # Create a playbook
ansible-playbook main.yml # Run the playbook
ansible-galaxy init <role-name> # Create a new role
# Playbook Format:
--- # Start with this
- hosts: web-servers # Host group
vars: # Variables
http_port: 80 # Key and value pair
roles: # Roles lists
- install
- configure
remote_user: root # Remote user for commands
tasks: # Tasks
- name: Install apache # Name of task
apt: # Ansible module
name: httpd # Name of package
notify: # Notify the handler
- restart apache # Handler name
handlers: # Handlers
- name: restart apache # Name of handle
service: # Handle's job
name: httpd
state: restarted
Command Module
command: bash script.sh # Simple command
expect: # Responses required
command: bash script.sh
responses:
Question:
- response1
- response2
Archives Module
archive: # Compress file
path: # Source files
- /path/to/foo
- /path/to/goo
format: gz OR zip OR bz2 # Custom format
dest: /path/to/fogo.tgz # Destination
unarchive:
src: foo.tgz # Source file or url
dest: /var/lib/foo
remote_src: yes # Source file already exist
Files Module
copy: # Copy files to remote host
src: /srv/myfiles/foo.conf
dest: /etc/foo.conf
owner: foo
group: foo
mode: '0644'
backup: yes # Backup original file
fetch: # Copy files from remote host
src: /tmp/somefile
dest: /tmp/fetched
file: # Change file properties
path: /etc/foo.conf
owner: foo
group: foo
mode: '0644'
file: # Change directory properties
path: /etc/some_directory
state: directory # Type of file
recurse: yes # Recursively change properties
owner: foo
group: foo
mode: '0755'
file: # Delelete file or directory
path: /etc/foo
state: absent
find: # Find files on remote host
paths: /tmp # Location to find
age: 2d # File Age (2d, 4w)
recurse: yes # Recursively change properties
size: 1m # Size of file
patterns: # Patterns of file
- '*.old'
- '*.log'
lineinfile: # Replace a line
path: /etc/selinux/config
regexp: '^SELINUX=' # Regex pattern
line: SELINUX=enforcing # Line after changes
Templates Module
template: # Jinja format templates
src: file.j2 # Source jinja file
dest: /etc/file.conf # Target file
owner: bin
group: wheel
mode: '0644'
backup: yes # Backup original file
Add {{ var_name }} in file.j2 to replace values dynamically
HTTP Module
get_url: # Get file from URL
url: http://example.com/path/file.conf
dest: /etc/foo.conf
mode: '0440'
checksum: sha256:basdasdasd # Checksum (sha256, md5)
uri: # Access a URL
url: http://www.example.com
return_content: yes # Verify status 200
Package Management Module
npm: # NPM package install
name: coffee-script # Package name
path: /app/location # Destination location
version: '1.6.1' # Package version
state: latest # absent # Update/Delete exisiting package
npm: # Install from package.json
path: /app/location # Location of package.json
pip: # PIP package install
name: # Package names list
- django
- bottle==1.01
executable: pip3.3 # pip or pip3
requirements: requirements.txt # Fix dependencies from file
Repository Module
apt:
update_cache: yes # apt update
autoclean: yes # apt clean
autoremove: yes # apt autoremove
apt: # APT install command
pkg: # Package names list
- nodejs
- curl
state: present # absent | latest # Install, delete or update
update_cache: yes # Update repository
force: no # Force action
apt: # Install from a .deb package
deb: "https://url/package.deb" # URL or location of deb
apt_repository: # Add a new repository
repo: "deb https://url main" # Repo URL
state: present # absent # Install or delete
yum: # YUM install
name: # Package name list
- httpd
- curl
state: present # latest | absent # Install, update, delete
yum: # RPM file install
name: package.rpm # Local file or URL
state: present # latest | absent # Install, update, delete
yum_repository: # Add a yum repository
name: epel # Repo name
baseurl: https://URL # Repo URL
gpgcheck: no # Verification
apk: # Alpine package install
name: foo # Package name
update_cache: yes # Update repository
System Module
service: # Service commands
name: httpd # Service name
state: started # stopped | restarted # Start, stop, restart
enabled: yes # Service enable
user: # Create User
name: john # Username
group: admin, wheel # Groups
shell: /bin/bash # Default shell
expires: 1422403387 # Expiration date
reboot: # Reboot the machine
reboot_timeout: 3600 # Timeout
Github Module
- git: # Clone a git repo
repo: git://github.com/ # Repo URL
dest: /srv/checkout # Destination location
version: master # Branch
Debug Playbooks
- debug: # Print custom messages
msg: "Hello {{ var }}"
Sources
- Ansible Community Documentation. https://docs.ansible.com/
- Ansible documentation, "How to build your inventory". https://docs.ansible.com/ansible/latest/inventory_guide/intro_inventory.html
Comments (1)
umam
Jan 14, 2025
nice
Leave a Reply
Comments are moderated. Please read our Comment Policy before posting.
Log in to post a comment.